Security in the traffic path
AI security should sit where decisions happen: between the application, retrieved context, tools, and model providers.
 Koreshield
 protects AI applications at runtime: prompts, retrieved context, provider calls, policy decisions, and the evidence teams need when security questions become business questions.
LLM applications do not fail like normal software. A model can obey a malicious instruction hidden in a document, leak sensitive data through a helpful answer, or call a tool under false context.
Koreshield is built as a runtime layer because the most important security decisions happen while traffic is moving, not after an incident review.
AI security should sit where decisions happen: between the application, retrieved context, tools, and model providers.
Prompts, responses, and evidence should be handled with minimisation and clear customer-controlled retention choices.
Teams need audit logs, policy decisions, and repeatable checks they can show to security, compliance, and legal reviewers.
Product, engineering, and AI governance ownership in one working team.
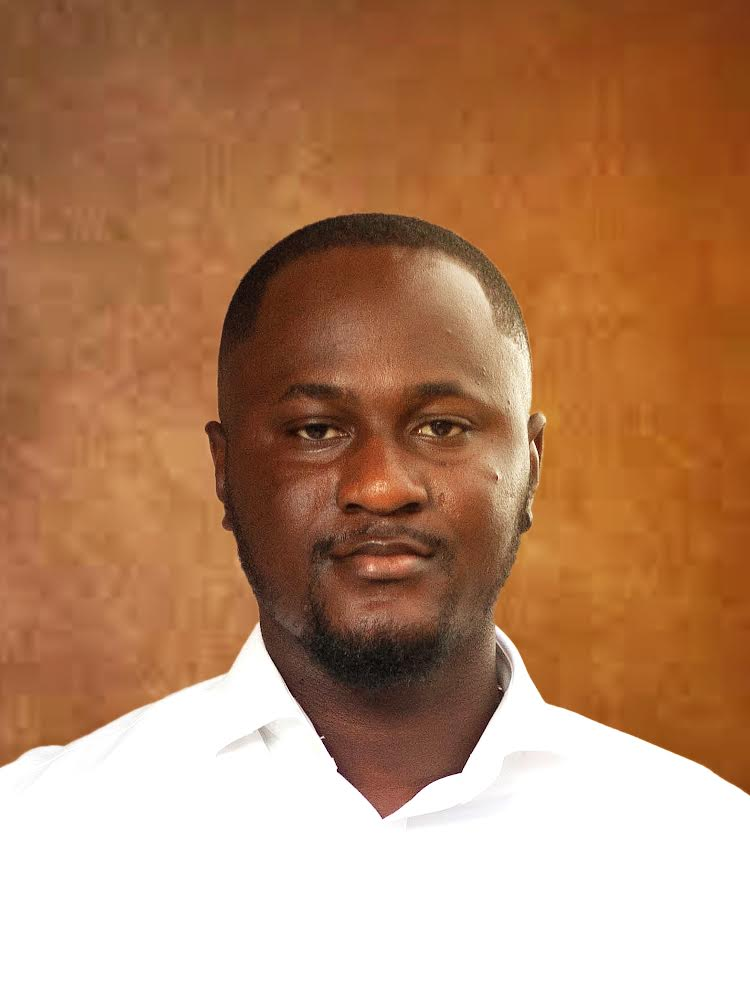
Leads product direction, customer discovery, and the commercial path for Koreshield.
LinkedIn
Architects the platform, SDKs, proxy layer, and operational infrastructure behind Koreshield.
LinkedIn
Shapes governance, risk, and compliance workflows so AI security evidence is usable by real organisations.
LinkedIn